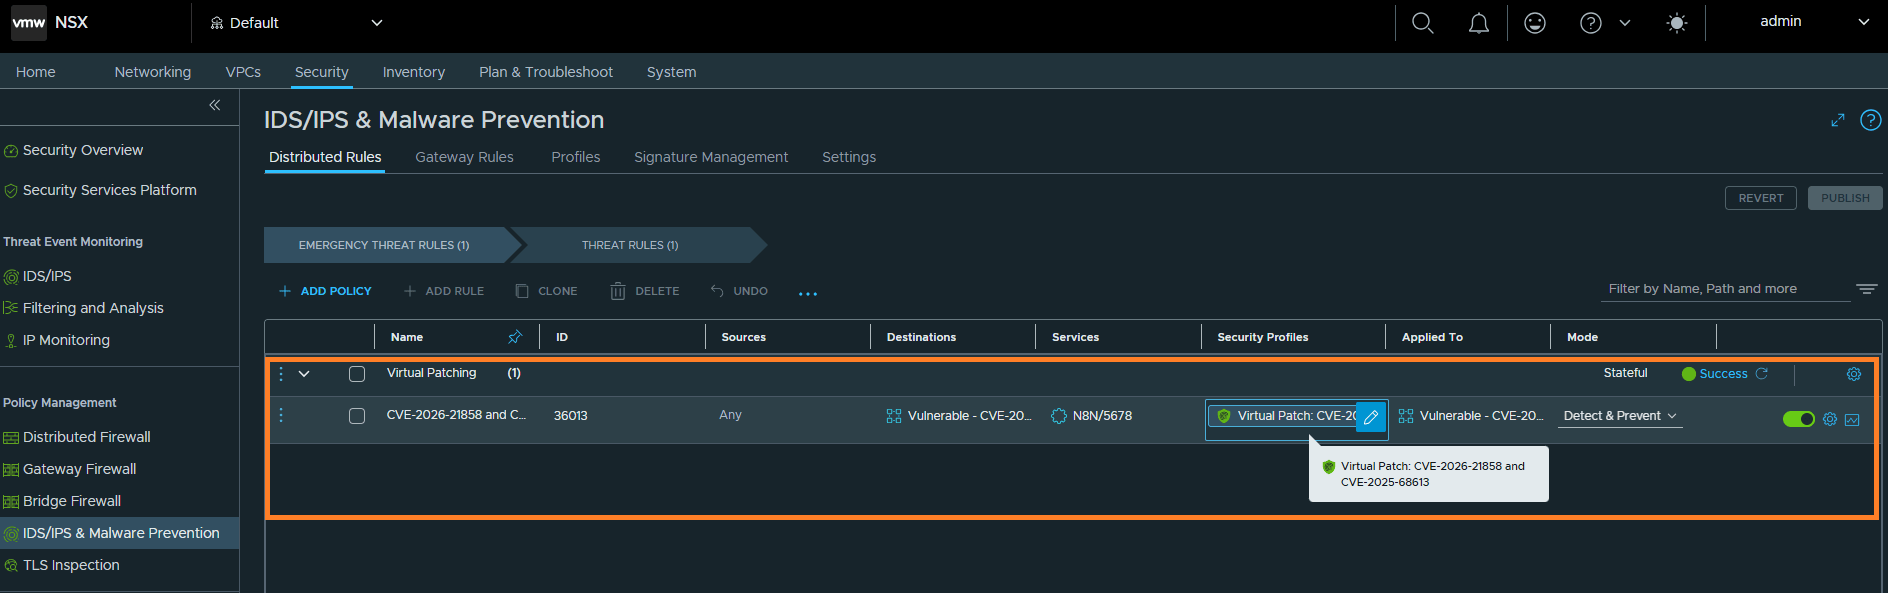
A short conversation to understand virtual patching using vDefend IDPS.
CuriousTechie: Hey ITGuy! I’ve been reading a lot about “Virtual Patching” recently. It sounds like some sort of magic shield for servers when a vulnerability is announced but the vendor hasn’t released a fix yet. What exactly is it?
ITGuy: “Magic shield” sounds really fancy! Virtual patching (sometimes called vulnerability shielding) is a security measure—or, in core infosec terms, a “compensating control”—that prevents the exploitation of a known vulnerability in an application or operating system without actually modifying the underlying source code or applying an official vendor patch.
Instead of updating the application itself, you place an enforcement layer—like an Intrusion Detection and Prevention System (IDPS) or a Web Application Firewall (WAF)—in front of it. This layer inspects incoming traffic, identifies the malicious packets trying to exploit the flaw, and blocks them before they ever reach the vulnerable application.
Continue reading “How to Implement Virtual Patching using VMware vDefend IDPS”
